A security incident rarely arrives in a neat sequence. A property manager may be dealing with an access-control alarm, an unsettled tenant, a missing patrol checkpoint, and an urgent call from a client at the same time. The team's response will depend less on whether everyone attended an annual briefing and more on whether people know who makes decisions, who communicates with the Security Operations Center, and who records what happened.
Security incident response training should therefore be treated as an operational discipline. Officers, supervisors, dispatchers, property staff, SOC analysts, and Guard Tour Management System operators need to practice coordination under incomplete information. The strongest programs use realistic scenarios, defined Incident Command System roles, and measurements that show whether the team is becoming faster and more accurate.
When the Worst Happens on Your Property
At 11:40 PM, a 14-story office tower is quiet except for the night shift. The SOC flags an unauthorized access attempt at the loading dock. At nearly the same moment, a uniformed officer encounters an agitated individual near a stairwell, while a tenant calls the front desk about a suspicious package.
Radio traffic overlaps. The supervisor can't immediately locate the officer. The dispatcher sees multiple alerts but isn't sure which one should be escalated first. The property manager receives partial information from several people, each describing a different part of the event.
No single procedure failed completely. The coordination system failed.
Many programs rehearse badge checks, patrol routes, and fire-drill movements because those activities are easy to observe. Those exercises have value, but they don't fully test the decisions that determine whether an incident remains controlled. A team must recognize competing priorities, establish authority, verify information, protect people, preserve evidence, and communicate without creating additional confusion.
Practical rule: Train people to make the next correct decision, not merely to repeat the next written step.
An incident response plan gives the team a starting point, but security incident response planning becomes useful only when officers and managers can operate it under pressure. The Incident Command System provides a practical backbone. It clarifies who has authority, how operations are assigned, how information is organized, and how outside agencies are brought into the response.
That structure works for cyber alerts, physical security events, workplace violence concerns, suspicious packages, construction-site injuries, and disruptions that cross several departments. The objective isn't to make every event look identical. It's to make the organization's decision process consistent when the facts are incomplete and priorities compete.
Defining Learning Objectives for Your Team
“Detect and escalate within 90 seconds” is a measurable objective. It names the action, the condition, and the performance standard supervisors can score during an exercise. Build the curriculum around objectives that show whether each role can make and communicate decisions under pressure.
Use these objectives as a working curriculum:
- Detect and escalate: When an officer observes a suspected security incident, the officer identifies the concern and escalates it within 90 seconds, using the approved radio or mobile reporting process.
- Establish command: When an incident requires coordinated action, the assigned supervisor establishes incident command in under three minutes, identifies the operating channel, and states the immediate priorities.
- Maintain a common operating picture: When several alerts arrive at once, the dispatcher or SOC analyst records verified facts, open questions, assigned resources, and pending decisions in a shared incident log.
- Deliver a verified situation report: When the SOC requests an update, the liaison officer provides confirmed information, labels unverified reports, and identifies the next required action.
- Preserve evidence: When an event may require investigation, officers protect relevant areas, avoid unnecessary contact with objects, and document the scene's condition.
- Use de-escalation: When a person is agitated or confrontational, the officer creates distance, uses calm communication, requests support, and follows the property's escalation thresholds.
- Complete documentation: After the scene is stabilized, each responsible person records a factual timeline, actions taken, notifications made, and unresolved follow-up items.
Curriculum topics should include threat recognition, radio discipline, escalation thresholds, evidence preservation, de-escalation, emergency notification, and post-incident reporting. Reports should answer who, what, when, where, why, and how, with the reason clearly identified when it is known. Security incident management reporting guidance reinforces objective, chronological documentation for follow-up, insurance records, and legal review.
Managers can align objectives with recognized role frameworks, including NIST NICE work roles or ASIS certification domains. Officer curricula, such as security officer training programs, can help connect those frameworks to assigned duties. The framework matters less than the operating discipline. Every objective should be rehearsed, scored, discussed, and linked to an improvement action.
Assign training by duty and repeat it through scheduled refreshers. The Canadian Centre for Cyber Security incident-response guidance supports role-based training, recurring instruction, and defined reporting periods for suspected incidents. This keeps response capability active rather than limiting it to onboarding.
Scenario-Based Exercises That Reflect Real Risks
A scenario should force decisions, not reward memorization. Start with the property's actual exposure, identify the people who would respond, and add information gradually. Supervisors can work through tabletop exercises, while officers practice radio traffic, movement, access control, and scene management during full-scale drills.
Residential communities
Begin with a domestic dispute in a leasing office. Shortly afterward, an unauthorized visitor tailgates through the resident gate. The first inject should test whether the concierge or officer separates the two concerns instead of treating them as one event. A later inject can introduce a resident's conflicting account, a blocked camera view, or a request from the leasing team to re-enter the office.
The exercise should test whether officers recognize the escalation threshold, protect uninvolved residents, notify the supervisor, and document the sequence. The supervisor must establish command, assign an officer to the gate, identify who speaks with property management, and ensure the SOC receives verified updates.
Retail centers
For a retail property, introduce an active aggressor event during peak customer activity, then add a simultaneous smash-and-grab at a storefront. The purpose isn't to simulate every tactical detail. It's to test competing priorities, public messaging, officer positioning, coordination with responding agencies, and the decision to preserve or restrict access to affected areas.
A red-team facilitator can create a radio outage or send conflicting information from a store employee. The team passes when it identifies the conflict, verifies facts through the SOC or supervisor, and avoids sending every available officer toward the same location.
Construction sites
A construction exercise might begin with a heat-injured worker near energized equipment. Add a near-miss crane incident, followed by a subcontractor dispute that becomes physical. The scenario tests life safety, site isolation, contractor coordination, evidence preservation, and the handoff to emergency responders.
The facilitator should record the time of each inject, the decision made, the person who made it, and the information available at that moment. That record turns a drill into an operational review rather than a subjective discussion.
| Property Type | Scenario Trigger | Key Decision Points | Expected Outcome |
|---|---|---|---|
| Residential community | Domestic dispute and gate tailgating | Separate incidents, protect residents, establish authority | Clear escalation, controlled access, accurate report |
| Retail center | Active aggressor event and smash-and-grab | Prioritize life safety, coordinate resources, manage public information | Unified response and verified agency handoff |
| Construction site | Worker injury near energized equipment | Isolate hazards, request medical support, preserve the scene | Safe stabilization and documented coordination |
Use tabletops for command staff and full-scale drills for field personnel. Add injects involving equipment failure, missed radio calls, unavailable supervisors, and conflicting priorities. The best exercise doesn't make the team feel successful because it followed a script. It shows whether the team can adapt when the script no longer fits.
Roles, Responsibilities, and the Command Structure
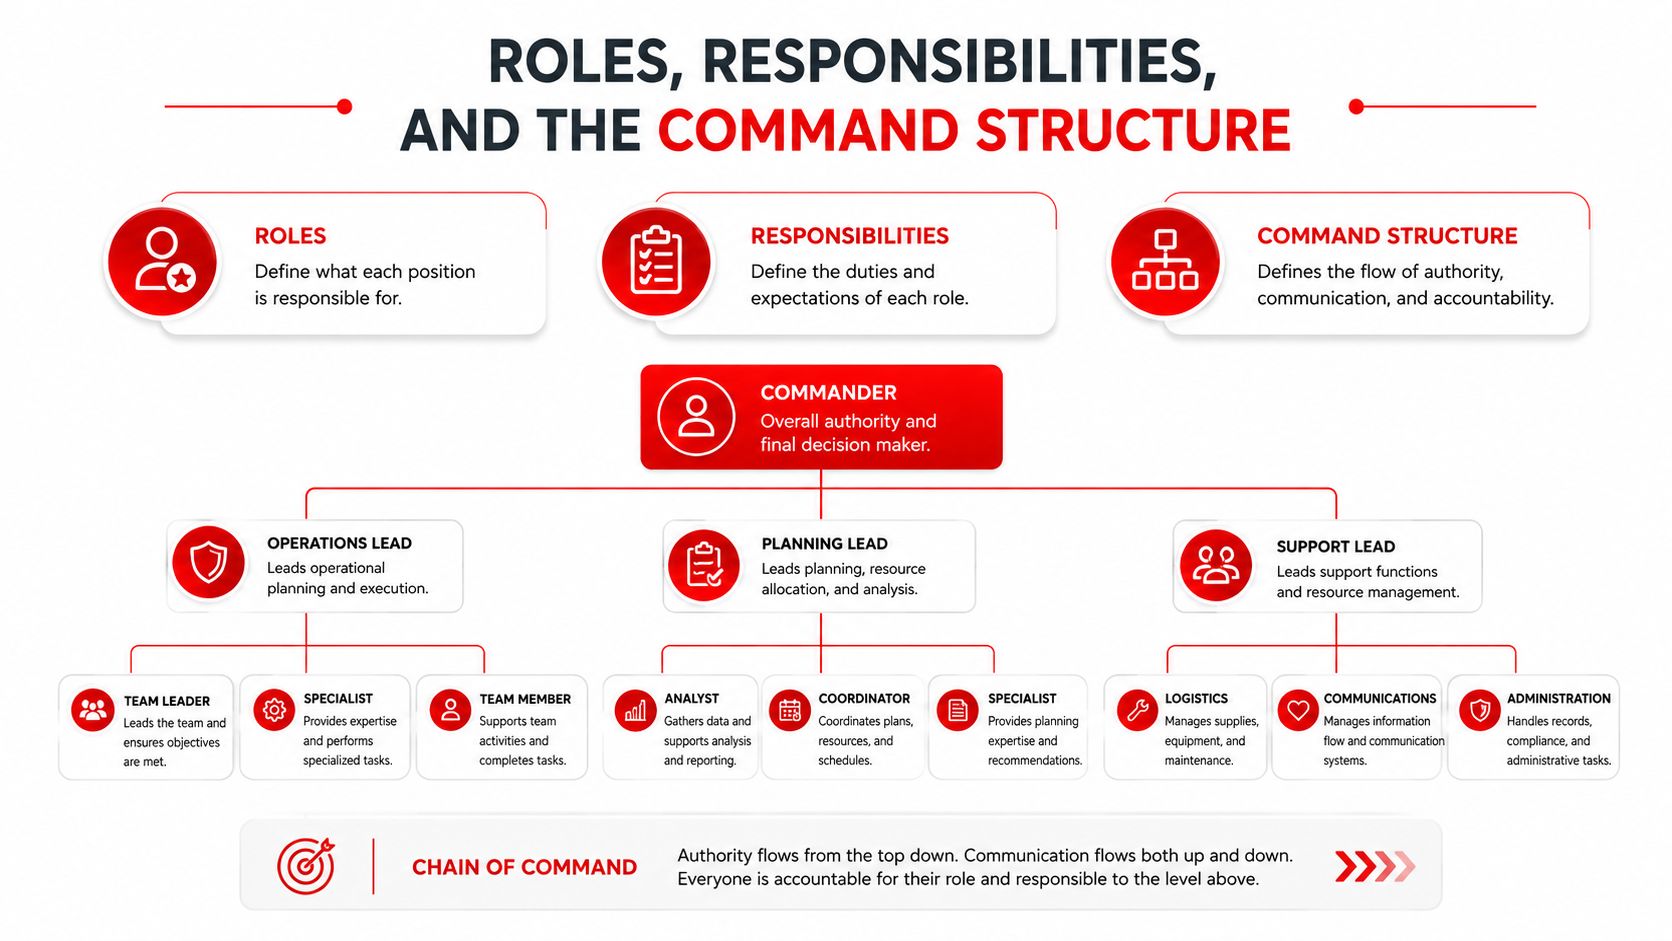
The Incident Command System works when it maps to the people already working the property. It shouldn't create a second organization that exists only on paper.
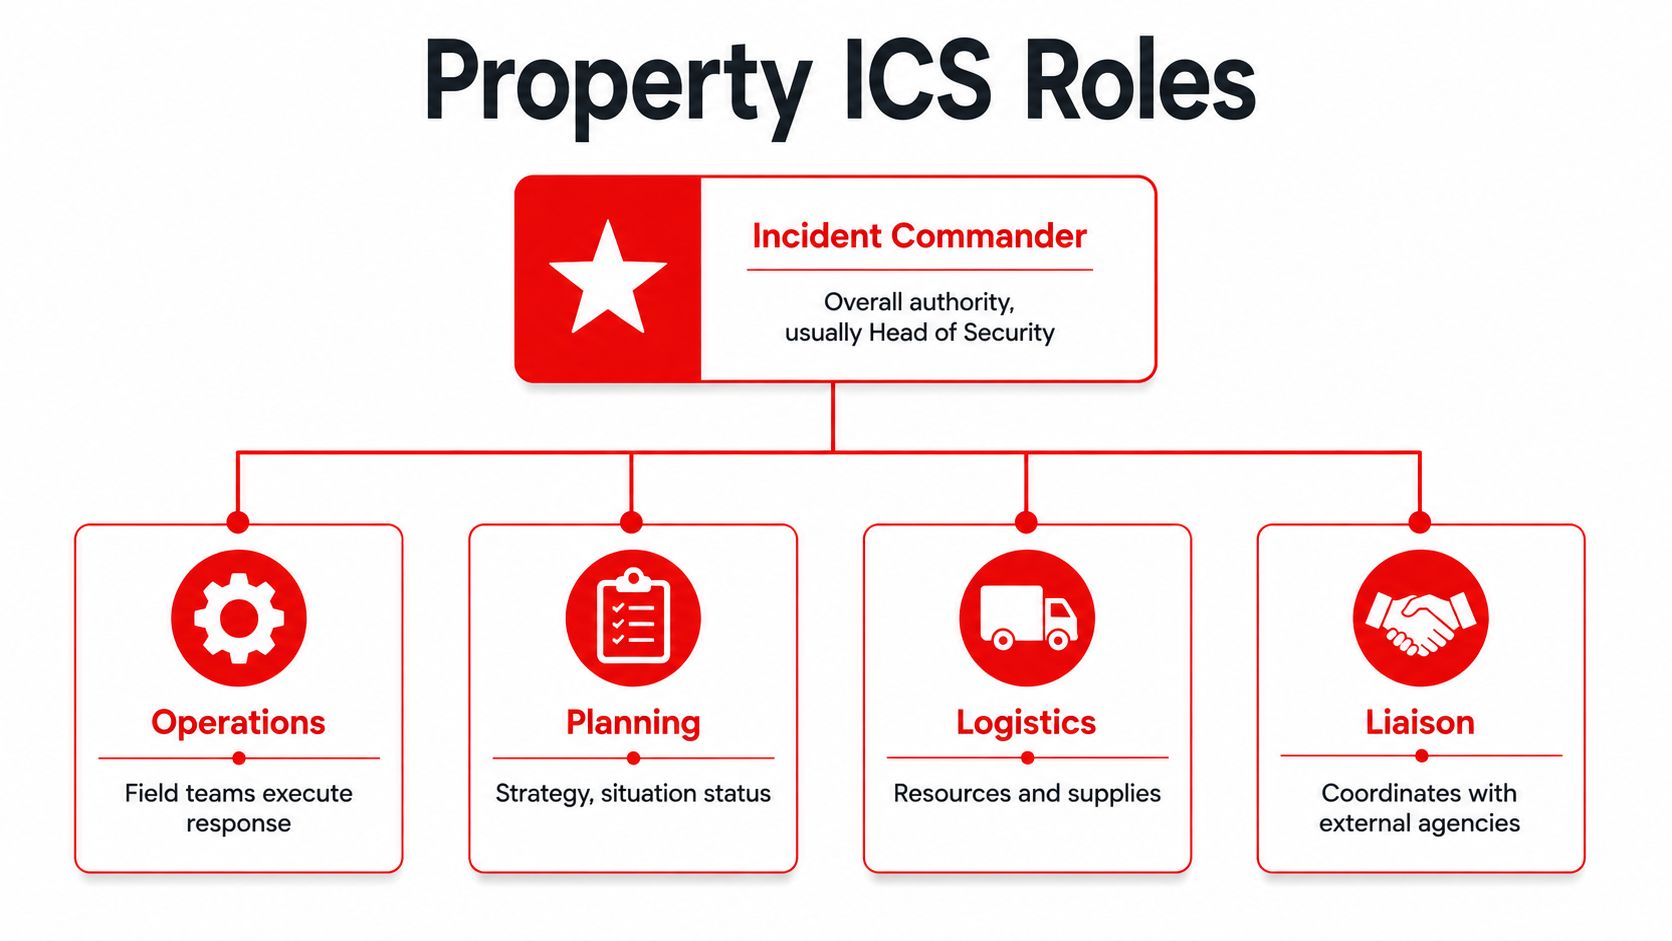
The Incident Commander sets priorities, approves major decisions, and communicates with property leadership. On a single property, that person may be the security supervisor or head of security. The property manager may support decisions involving tenants, building operations, access restrictions, or business continuity.
Operations directs field activity. The lead officer, patrol supervisor, concierge, or site safety lead may fill this function depending on the event. Planning maintains the situation status, incident timeline, maps, camera information, and unresolved questions. The SOC analyst or dispatcher often supports this work.
Logistics identifies resources, equipment, access credentials, barriers, radios, transportation, and relief staffing. Liaison coordinates with police, fire, emergency medical services, vendors, contractors, and client representatives. A GTMS operator supports accountability by confirming checkpoint activity, exception handling, officer acknowledgments, and report completion.
A practical responsibility matrix
| Response phase | Decides | Executes | Advises | Must be informed |
|---|---|---|---|---|
| Initial detection | Supervisor or designated IC | Reporting officer and SOC analyst | Dispatcher, property manager | Client contact |
| Scene stabilization | Incident Commander | Operations and field officers | SOC, facilities, emergency services | Property leadership |
| External coordination | Liaison or IC | Liaison and assigned supervisor | Police, fire, medical, legal contacts | Client and relevant stakeholders |
| Documentation | Assigned report owner | Officer, dispatcher, GTMS operator | Supervisor and SOC | Property manager |
| After-action review | Account leader or IC | Planning and responsible department | Officers, SOC, GTMS operator | Client leadership |
Span of control matters. A supervisor who is directing field officers, answering tenant calls, reviewing camera feeds, and writing the incident log will eventually miss something. Training should expose that overload and teach the team when to create a separate planning, logistics, or liaison assignment.
The structure should also support unified command when public safety agencies arrive. The security team doesn't surrender useful information, but it does coordinate authority and objectives with the responding agency. Managers looking for additional organizational guidance can review these steps to form a security response team, particularly when defining internal and external responsibilities.
Role swaps belong in every mature program. Have the SOC analyst take the liaison position, let a patrol supervisor work planning, and test what happens when the primary incident commander becomes unavailable. Every seat needs a backup, and every person needs to understand the documentation duties attached to the role.
Connecting Training to SOC Monitoring and GTMS
The field officer, SOC, and Guard Tour Management System should operate as one response loop. If each system produces a separate record that nobody reconciles, the organization may have more information but less control.
Consider a missed GTMS checkpoint at 02:14. The SOC analyst reviews the exception, checks the officer's last known activity, and contacts the assigned officer through the approved channel. The officer acknowledges through the mobile application, explains the exception, and receives a dispatch instruction if a physical check is required.
The supervisor is notified when the exception indicates a possible incident rather than a routine delay. The Incident Commander decides whether to expand the response, while the SOC pulls relevant video and records the timestamps. Once the event is stabilized, the officer completes a digital activity report with photos or supporting details, and the GTMS record flows into the post-incident review.
Exercise the handoffs, not just the devices
A tabletop should test the decision path before anyone enters the field:
- GTMS exception: Can the SOC identify whether a missed checkpoint is a scheduling issue, equipment issue, or welfare concern?
- Officer acknowledgment: Can the assigned officer receive, understand, and confirm the dispatch instruction?
- Escalation tree: Does the SOC platform identify the correct supervisor, client contact, and external agency pathway?
- Video retrieval: Can the analyst locate and share relevant footage without delaying the field response?
- Radio discipline: Does the team use a designated channel and keep messages concise?
- Report closure: Does the supervisor verify that the exception, incident report, photos, and follow-up tasks align?
The process should include an out-of-band communication option if the primary platform is unavailable. Secure communication planning, access control, and data handling also deserve attention. Teams reviewing workforce or vendor data can use resources such as WorkSignal data security as a reference point for discussing how operational information should be protected.
Overton Security provides a model that combines 24/7 SOC oversight, GPS-enabled patrol accountability, NFC checkpoint scans, digital Daily Activity Reports, photos, dispatch support, and incident escalation. That combination can be useful when training focuses on the complete loop, from detection through documented follow-up. Managers can also review security operations center best practices when shaping monitoring and escalation exercises.
Evaluation Metrics, Compliance, and Sample Schedules
Attendance proves that people were present. It doesn't prove that they can perform. A useful evaluation program measures the time and quality of decisions that matter during an incident.
Track mean time to acknowledge, time to establish command, correct escalation percentage, scenario checklist performance, GTMS exception closure, and closure of after-action items within the required review period. The exact target should reflect the site's risk profile and staffing model. The important point is to define the target before the exercise and score the same behaviors each time.
Recent simulation data cited by Evocatus Consulting found 22% accuracy during cyber simulations, 29 hours to contain an infection, and 60% of training activity focused on vulnerabilities older than two years. The same source reported that only 41% of organizations included non-technical functions such as legal, HR, communications, or senior executives in simulations. These findings support a practical conclusion, completion and confidence metrics can hide serious coordination gaps. Simulation measurement guidance recommends measuring decision latency, communication breakdowns, and resilience rather than attendance alone.
Compliance and records
Training should align with the hazards and legal duties that apply to the property. For hazardous substance incidents, review OSHA 29 CFR 1910.120(q) requirements with qualified safety and compliance professionals. ASIS standards, state licensing rules, client contracts, insurance requirements, and site-specific post orders may also affect curriculum design and records.
Keep:
- Attendance and role assignment records: Show who trained, which role they practiced, and when refresher instruction occurred.
- Scenario results: Record response times, missed decisions, communication errors, and checklist outcomes.
- Evidence-handling notes: Document how the team protected the scene and preserved relevant information.
- After-action assignments: Name an owner, due date, corrective action, and verification method.
- Qualification records: Maintain required licenses, certifications, background screening, and role-specific authorizations. Programs involving volunteers or temporary site access should define screening expectations, including an appropriate volunteer background check process where applicable.
Sample quarterly schedule
| Quarter Week | Drill Type | Duration | Owner | Pass Criteria |
|---|---|---|---|---|
| First week | Objectives and escalation review | One planning session | Security manager | Roles, contacts, and thresholds verified |
| Fifth week | Supervisor tabletop | One tabletop session | Incident Commander | Command established and decisions logged |
| Ninth week | Officer communications drill | One field session | Patrol supervisor | Radio, dispatch, and reporting steps completed |
| Thirteenth week | Full-scale property exercise | One exercise block | Account leadership | Scenario objectives met and actions assigned |
For a high-attrition retail or construction site, use shorter monthly micro-drills. A supervisor can run a brief radio and escalation test during a shift, the SOC can test a GTMS exception, and the site manager can review one report for factual completeness. Short exercises work when they're regular, scored, and connected to the next training need.
Key Takeaways and Next Steps
A reliable program gives people a shared way to think before it gives them more procedures. The Incident Command System establishes authority and coordination. Scenario-based exercises turn that structure into practiced behavior. SOC monitoring and GTMS records provide the operational evidence needed to see where the response slowed or became unclear.
Before scheduling the first exercise, confirm these items:
- Learning objectives: Each objective names the role, action, condition, and performance standard.
- Scenario library: The property has scenarios covering its top three incident types, including at least one cross-functional event.
- Escalation paths: Officers, supervisors, SOC analysts, GTMS operators, property managers, and outside responders know who receives each type of report.
- Role coverage: Every command and support position has a trained backup, and exercises include role swaps.
- Review cadence: Tabletop exercises, field drills, after-action reviews, and corrective-action tracking sit inside the regular security operating rhythm.
Australian government posture reporting shows why preparedness needs both a plan and recurring training. In its 2025 report, 90% of entities had an incident response plan, compared with 86% in 2024, while 87% provided annual cybersecurity training, compared with 78% in 2024. Privileged-user training moved in the opposite direction, with 45% providing annual training in 2025, compared with 51% the year before, showing that advanced-role readiness can remain uneven even as baseline preparedness improves. These figures are summarized with the Commonwealth Cyber Security Posture reporting.
Schedule the first tabletop within 30 days, assign one accountable owner, and select a scenario that forces the team to coordinate across property staff, field officers, the SOC, and GTMS operators. Then measure acknowledgment time, escalation accuracy, command establishment, and corrective-action closure. A recurring discipline will tell you far more than an annual attendance sheet.
If your team needs help designing role-specific exercises, Overton Security can support onsite guards, unarmed officers, mobile patrols, 24/7 SOC oversight, GPS-enabled GTMS reporting, and customized post orders for residential, retail, construction, and commercial properties. Visit Overton Security to discuss a practical incident response training program for your property or portfolio.